外掛說明
真正的網頁應用程式防火牆
NinjaFirewall (WP Edition) 是真正的網頁應用程式防火牆。安裝與設定就像一般外掛一樣簡單,但它能獨立運作,在請求進入 WordPress 之前提供防護。
透過 NinjaFirewall,網站管理員也能使用通常只有 Apache ModSecurity 模組或 PHP Suhosin 擴充功能等安全性工具才具備的進階防護功能。
NinjaFirewall 需要 PHP 7.1 以上版本及 MySQLi 擴充功能,僅支援 Unix 類作業系統(如 Linux、BSD),不支援 Microsoft Windows。
當 HTTP/HTTPS 請求傳送至 PHP 指令碼時,NinjaFirewall 會在請求到達 WordPress 或任何外掛之前,先行攔截、掃描、清理或拒絕。防護範圍涵蓋網站安裝目錄及子目錄中的所有指令碼,包括不屬於 WordPress 套件的指令碼。即使請求的目標是經過編碼保護的 PHP 指令碼,或是駭客植入的 Shell 指令碼與後門,NinjaFirewall 也能加以過濾。
強大的過濾引擎
NinjaFirewall 內建功能強大的 WordPress 外掛過濾引擎。其核心功能是將傳入 HTTP 請求的資料正規化並轉換,藉此偵測駭客用來規避網頁應用程式防火牆的技術與混淆手法,同時支援及解碼多種編碼格式。完整介紹請參閱我們的部落格:NinjaFirewall 過濾引擎簡介。
快速且有效的 WordPress 暴力破解攻擊防護
NinjaFirewall 會在網站與任何外掛之前處理傳入的 HTTP 請求,因此是唯一能防護大規模暴力破解攻擊的 WordPress 外掛,包括來自數千個不同 IP 的分散式攻擊。
請參閱我們的效能與壓力測試:暴力破解攻擊偵測外掛比較
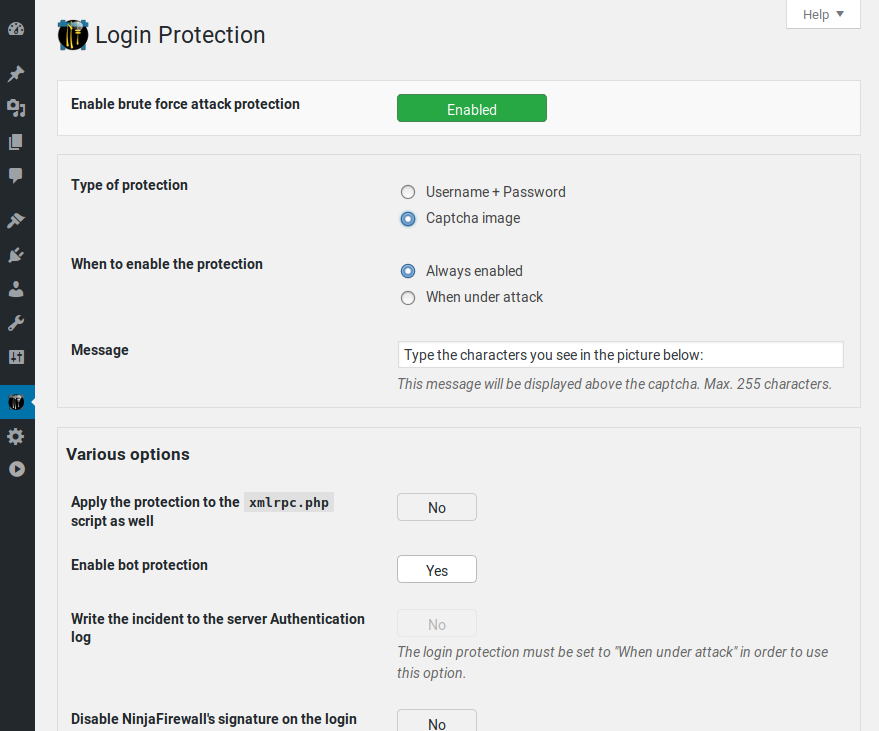
這項防護適用於 wp-login.php 指令碼,也可延伸至 xmlrpc.php。事件也能寫入伺服器的 AUTH 記錄檔,方便系統管理員進行監控,或在伺服器層級封鎖 IP(例如使用 Fail2ban)。
即時偵測
檔案防護是 NinjaFirewall 提供的獨有即時偵測功能,可即時偵測對近期修改或建立的 PHP 檔案的任何存取,並發出警示。如果駭客將 Shell 指令碼上傳至網站(或在現有檔案中植入後門),再嘗試透過瀏覽器或指令碼直接存取該檔案,NinjaFirewall 就會攔截該 HTTP 請求,立即偵測到這是近期修改或建立的檔案,並傳送包含完整詳細資料(指令碼名稱、IP、請求、日期與時間)的警示。
檔案完整性監控
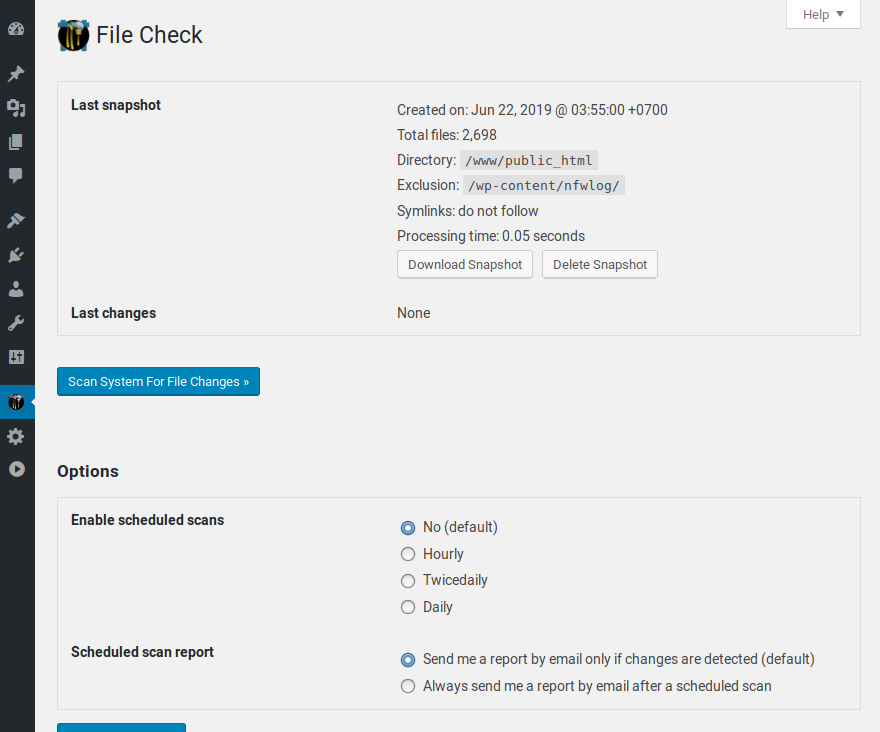
檔案檢查可每小時、每天兩次或每天掃描網站,監控檔案完整性。任何檔案變更都能偵測,包括檔案內容、權限、擁有權、時間戳記,以及檔案的建立與刪除。
即時監看網站流量
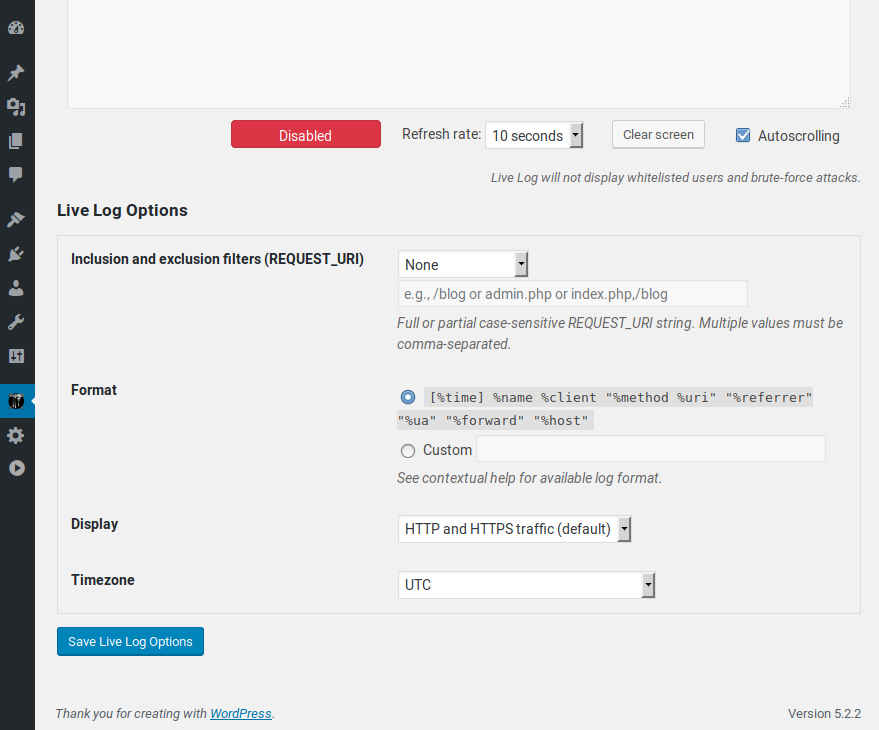
即時記錄可讓您即時監看網站流量,並以類似 Unix 指令 tail -f 的格式顯示連線。由於它直接與防火牆通訊,不需要載入 WordPress,因此即時記錄執行快速、輕巧,即使將重新整理間隔設為最低值,也不會影響伺服器負載。
事件通知
NinjaFirewall 可在網站發生特定事件時,透過電子郵件發出警示。部分警示預設已啟用,強烈建議保持啟用。駭客入侵 WordPress 管理控制台後,常會安裝或上傳含有後門的外掛或佈景主題,藉此完全掌控網站。NinjaFirewall 也能在重要通知中附加 PHP 回溯追蹤資訊。
監控的事件:
- 網站管理員登入。
- 資料庫中的任何網站管理員帳號遭到修改。
- 外掛上傳、安裝、啟用/停用、更新、刪除。
- 佈景主題上傳、安裝、啟用、刪除。
- WordPress 更新。
- 外掛與佈景主題有待安裝的安全性更新。
持續防護新發現的 WordPress 安全性漏洞
為提供有效的防護,NinjaFirewall 可每天、每天兩次,甚至每小時自動更新安全性規則。每當 WordPress 或其外掛/佈景主題發現新的安全性漏洞,就會提供一組新的安全性規則,立即保護您的網站。
完善的隱私保護
與雲端網頁應用程式防火牆(Cloud WAF)不同,NinjaFirewall 會在您自己的伺服器與基礎架構上執行並過濾流量。這表示敏感資料(聯絡表單訊息、顧客信用卡號、登入憑證等)會留在您的伺服器上,不會經由第三方公司的伺服器傳送,避免不必要的風險(例如為檢查 HTTPS 流量而將其解密、員工以純文字存取您的資料或記錄、私人資訊遭竊、中間人攻擊等)。
網站可以在執行 NinjaFirewall 的同時,符合《一般資料保護規則》(GDPR)。請參閱我們的部落格以瞭解詳細資訊。
IPv6 相容性
IPv6 相容性是安全性外掛必備的功能:若只支援 IPv4,駭客便能透過 IPv6 輕易繞過外掛。NinjaFirewall 原生支援 IPv4 與 IPv6 通訊協定,涵蓋公用與私有位址。
多站網路支援
NinjaFirewall 相容於多站網路,會保護網路中的所有網站,而且只有多站網路管理員能從網路主網站存取設定介面。
可在防火牆執行前加入自己的 PHP 程式碼
您可以透過選用的分散式設定檔,在防火牆執行前加入自己的 PHP 程式碼。這些程式碼會在 WordPress 及其所有外掛載入前處理。這項功能非常強大,幾乎不限制用途,例如新增自己的安全性規則、處理 HTTP 請求與變數等。
低資源需求的防火牆
NinjaFirewall 經過最佳化,執行快速、體積精簡,所需系統資源極低。
您可以親自測試:下載並安裝 Code Profiler 外掛,比較 NinjaFirewall 與其他安全性外掛的效能。
不干擾操作的使用者介面
NinjaFirewall 的外觀與操作方式就像 WordPress 的內建功能。介面不含干擾操作的橫幅、警告或刺眼的色彩,採用 WordPress 簡潔清楚的介面,也方便在智慧型手機上使用。
情境說明
NinjaFirewall 的每個選單頁面都提供情境說明,包含實用的操作與設定資訊。
如需協助,請按一下管理面板各頁面右上角的 [使用說明] 選單分頁。
需要更完善的安全防護嗎?
歡迎瞭解我們全新推出的強化版本:NinjaFirewall WP+ Edition
- 使用 Unix 共用記憶體進行處理程序間通訊,提供快速效能。
- IP 存取控制。
- 角色型存取控制。
- 依國家進行存取控制(透過地理位置判斷)。
- URL 存取控制。
- 機器人存取控制。
- 透過 WP-CLI 匯入/匯出設定。
- 集中式記錄。
- 留言與使用者註冊表單的垃圾訊息防護。
- 速率限制選項,可封鎖惡意機器人、爬蟲、網頁擷取程式與 HTTP 攻擊。
- 回應本文過濾器,可在 HTML 頁面輸出傳送至訪客瀏覽器之前進行掃描。
- 更完善的檔案上傳管理。
- 更完善的記錄檔管理。
- Syslog 記錄。
進一步瞭解 WP+ Edition 的獨有功能。比較 WP 與 WP+ Edition。
系統需求
- WordPress 4.9+
- 具備
manage_options及unfiltered_html capabilities權限的網站管理員/多站網路管理員。 - PHP 7.1+
- MySQL 或 MariaDB,搭配 MySQLi 擴充功能
- 相容於 Apache / Nginx / LiteSpeed / Openlitespeed
- 僅支援 Unix 類作業系統(Linux、BSD 等)。NinjaFirewall 不相容於 Microsoft Windows。
螢幕擷圖
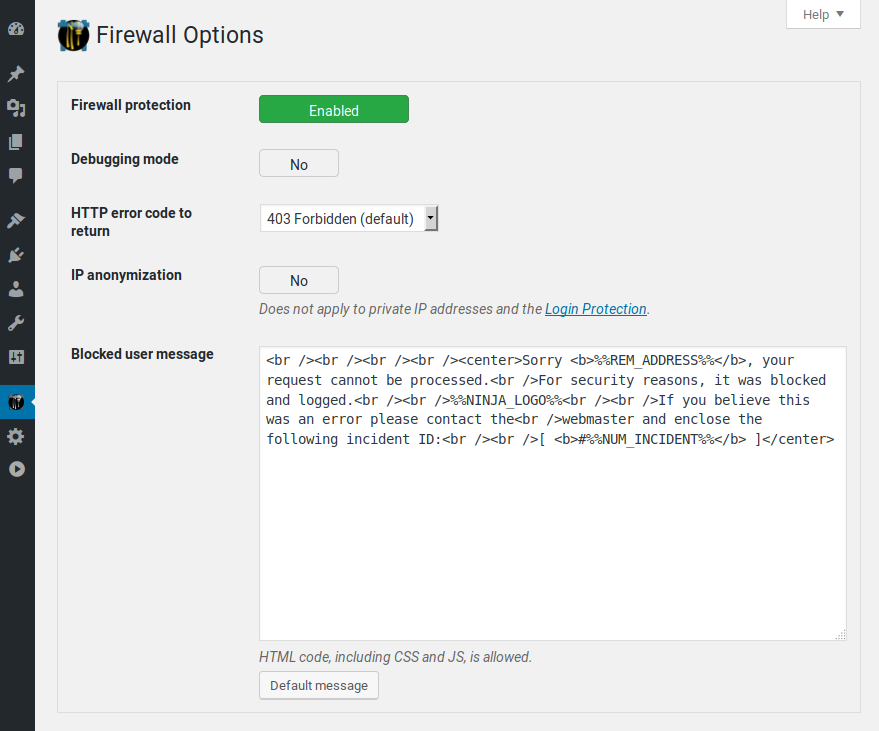
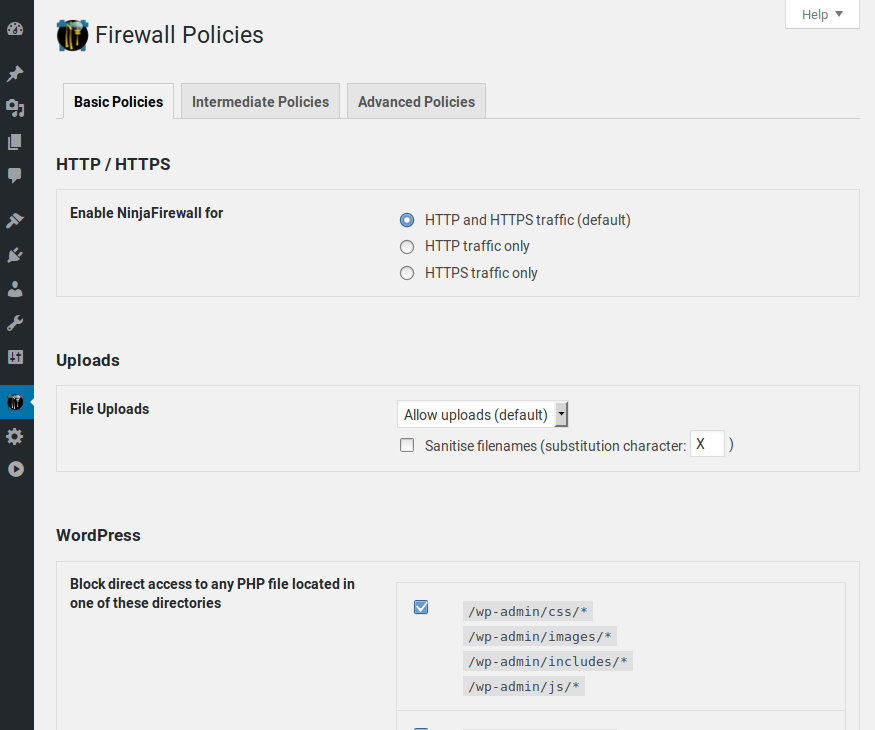
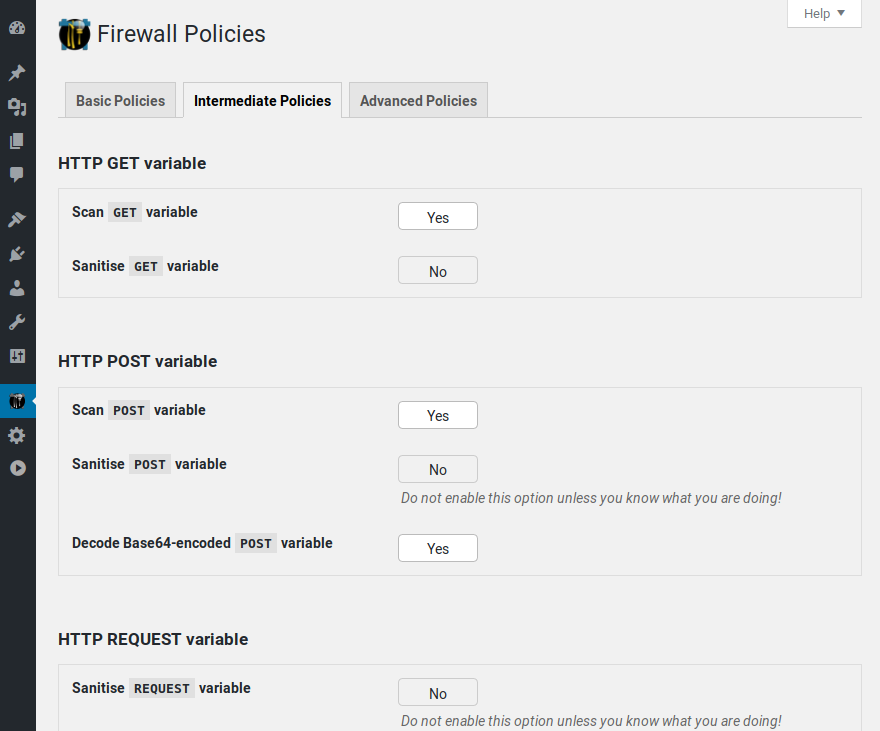

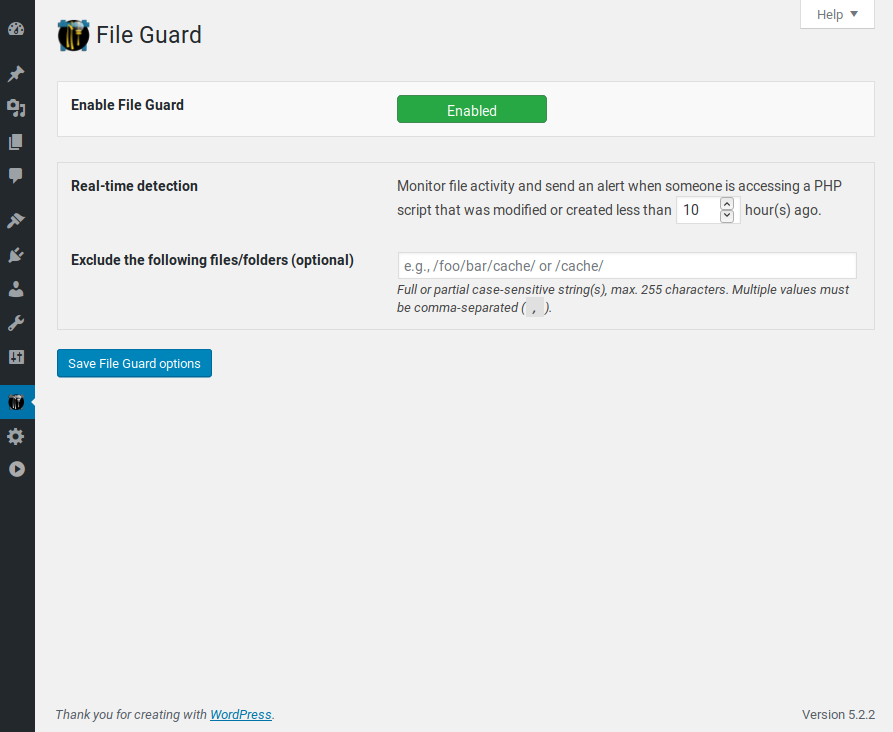

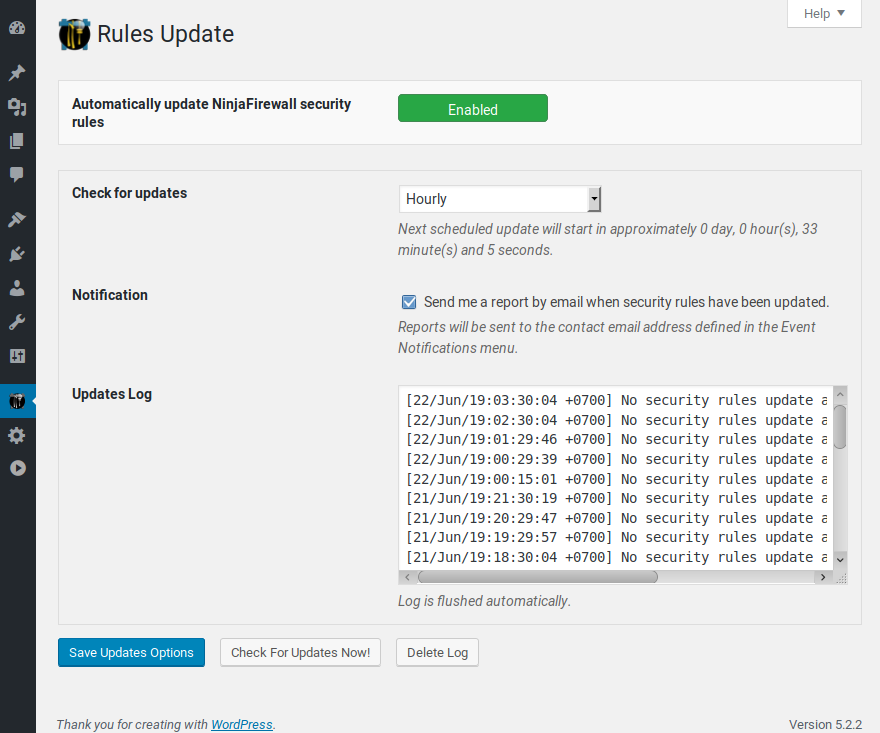
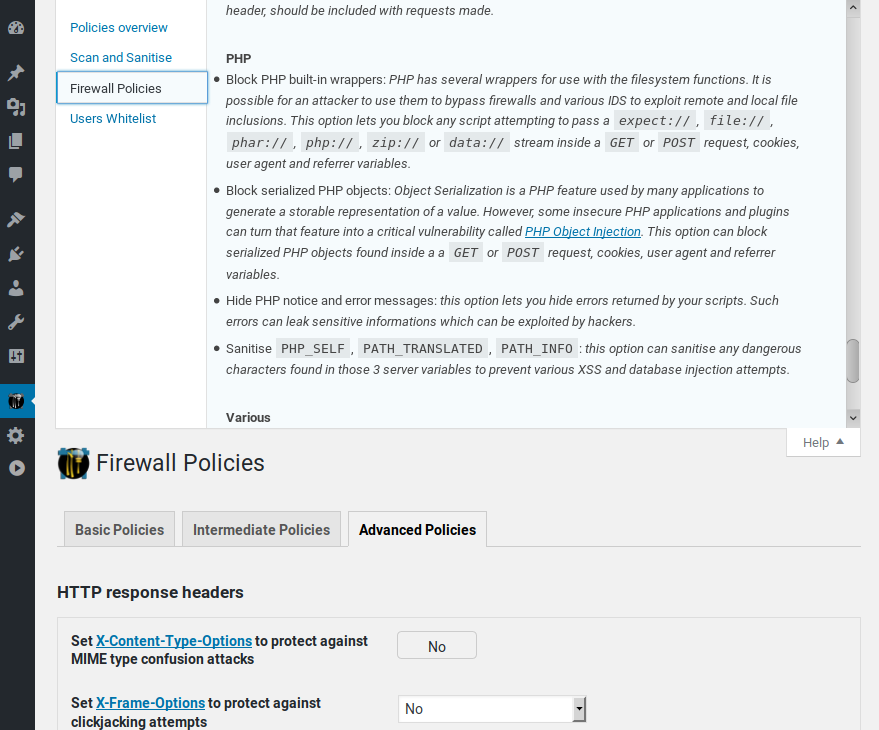
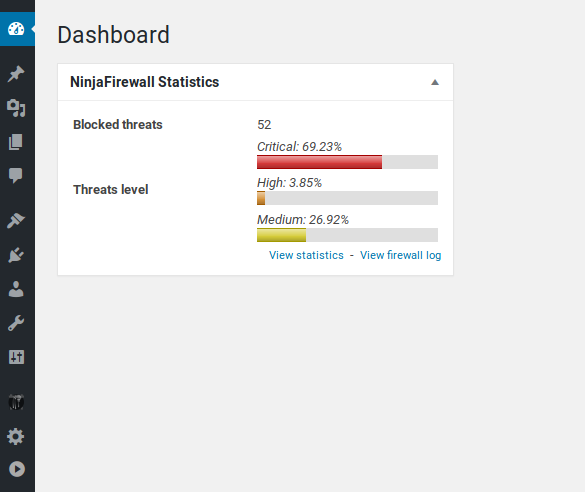
安裝方式
- 將
ninjafirewall資料夾上傳至/wp-content/plugins/目錄。 - 透過 WordPress 的 [外掛] 選單啟用外掛。
- 外掛設定位於 [NinjaFirewall] 選單中。
常見問題集
-
NinjaFirewall 與其他 WordPress 安全性外掛有何不同?
-
NinjaFirewall 位於攻擊者與 WordPress 之間,能在請求到達網站及任何外掛之前先進行過濾。運作方式如下:
Visitor -> HTTP server -> PHP -> NinjaFirewall #1 -> WordPress -> NinjaFirewall #2 -> Plugins & Themes -> WordPress exit -> NinjaFirewall #3以下是所有 WordPress 外掛的運作方式:
Visitor > HTTP server > PHP > WordPress > Plugins -> WordPress exit與其他安全性外掛不同,NinjaFirewall 會保護所有 PHP 指令碼,包括不屬於 WordPress 套件的指令碼。
-
NinjaFirewall 的防護能力如何?
-
NinjaFirewall 內建強大的過濾引擎,可偵測駭客用來規避網頁應用程式防火牆的技術與混淆手法,並支援及解碼多種編碼格式。完整介紹請參閱我們的部落格:NinjaFirewall 3.0 過濾引擎簡介。
-
安裝 NinjaFirewall 需要 root 權限嗎?
-
NinjaFirewall 不需要任何 root 權限,且完全相容於共用主機帳號。您可以像安裝一般外掛一樣,從 WordPress 管理控制台安裝。
-
可以搭配 Nginx 使用嗎?
-
NinjaFirewall 可搭配 Nginx 及其他以 Unix 為基礎的 HTTP 伺服器(Apache、LiteSpeed 等)使用。安裝程式會自動偵測。
-
需要修改 PHP 指令碼嗎?
-
不需要修改任何指令碼。NinjaFirewall 會在所有請求到達指令碼之前攔截並處理。即使是經過編碼保護的指令碼(ionCube、ZendGuard、SourceGuardian 等),也能正常運作。
-
我已將 wp-config.php 檔案移至其他目錄,NinjaFirewall 還能正常運作嗎?
-
NinjaFirewall 會在目前資料夾中尋找 wp-config.php 指令碼;若找不到,則會在上層資料夾中尋找。
-
如果網站使用 Cloudflare 等 CDN 服務,NinjaFirewall 能偵測到訪客的正確 IP 嗎?
-
您可以透過選用的設定檔,指定 NinjaFirewall 要使用哪個 IP。請依照這些步驟操作。
-
會拖慢網站速度嗎?
-
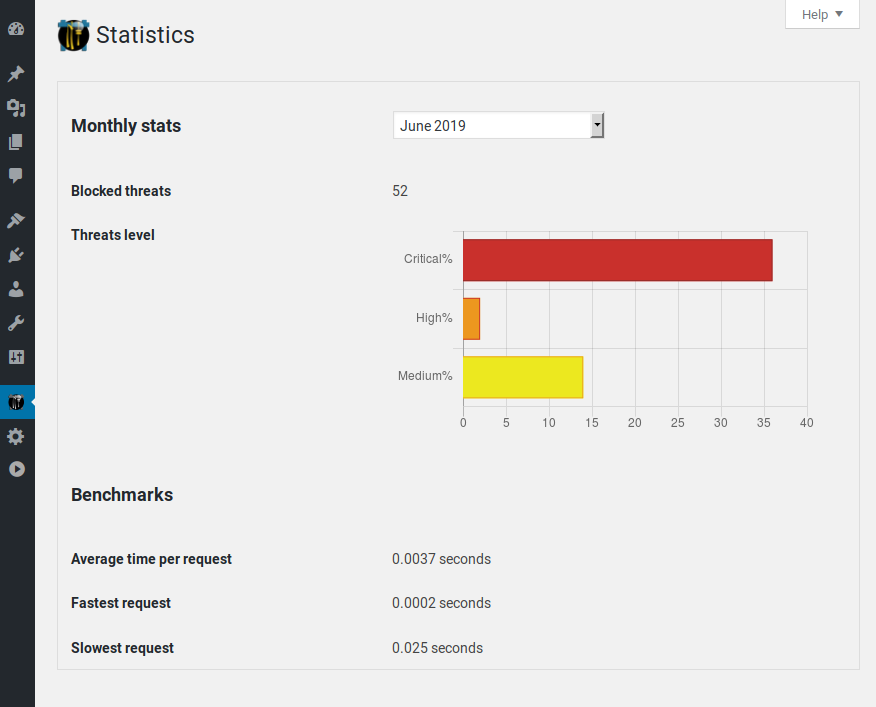
無論是否使用 NinjaFirewall,訪客都不會感受到差異。您可以在 WordPress 管理控制台中,按一下 [NinjaFirewall > 狀態] 選單,查看效能測試與統計資料(每個請求的最短、最長及平均處理時間)。NinjaFirewall 經過最佳化,執行快速、體積精簡,所需系統資源極低,且效能優於其他所有安全性外掛。
在 WordPress 載入前封鎖危險請求與機器人,可節省頻寬並降低伺服器負載。 -
有 Microsoft Windows 版本嗎?
-
NinjaFirewall 僅能在 Unix 類伺服器上執行。目前沒有 Microsoft Windows 版本,也沒有推出的計畫。
使用者評論


參與者及開發者


變更記錄
Need more security? Take the time to explore our supercharged Premium edition: NinjaFirewall WP+ Edition
4.9.2
- Fixed bugs related to the login protection, the user ennumeration REST API hook and the firewall statistics file.
- WP+ Edition (Premium): Updated IP location databases.
4.9.1
- Behind-the-scenes update: A lot of code was rewritten in this release to make NinjaFirewall better. That includes Centralised Logging, Login Protection, File Guard, rules and notification update, configuration import/export, firewall engine (data transformation and normalization) etc., as well as many small fixes and adjustments.
4.9
- Improved the security updates notification.
- WP+ Edition (Premium): Fixed a bug where the dashboard may not always show a warning if the admin is not whitelisted.
- The “Sanitise POST variable” and “Sanitise REQUEST variable” policies were removed.
- Some little modifications to the UI of the plugin.
- It is no longer possible to configure NinjaFirewall to use PHP sessions; If your site was using such configuration, it will automatically switch to NinjaFirewall sessions instead, which were introduced several months ago and are a much better option.
- WP+ Edition (Premium): Updated IP location databases.
- Many small fixes and adjustments.
4.8.8
- Because WordPress.org enforces a mandatory 24-hour update delay on all new plugin releases, as soon as a new security updates is available for a plugin, NinjaFirewall will allow you to update it immediately from the “Plugins” page.
- Small fixes and adjustments.
4.8.7
- Fixed a PHP warning in File Check.
- Fixed a potential “Allowed memory size exhausted” error.
- Several small fixes and adjustments under the hood.
- WP+ Edition (Premium): Updates Stripe and Airwallex webhook notification IP addresses in the Access Control section.
- WP+ Edition (Premium): Updated list of banned bots in the Access Control section.
4.8.6
- Many small fixes and adjustments to make NinjaFirewall better.
- Renamed/standardised all filenames to improve project readability and maintainability.
- Errors occurring during the firewall activation will be displayed with all details.
- WP+ Edition (Premium): the bot list is now sorted in alphabetic order.
- WP+ Edition (Premium): Updated IP location databases.
4.8.5
- Behind-the-scenes update: All the code dealing with exporting, importing and restoring the configuration was rewritten.
- WP+ Edition (Premium): You can import/export the configuration from WP-CLI. See
$ wp ninjafirewall helpfor usage.
4.8.4
- Behind-the-scenes update: All the code dealing with the firewall log and IP address checks has been rewritten, bugs were resolved and several small fixes were added to make NinjaFirewall better.
- WP+ Edition (Premium): Updated IP location databases.
4.8.3
- When running in “Full WAF mode”, NinjaFirewall will automatically detect if the SQL database is listening on IPv6.
- WP+ Edition (Premium): Updated IP location databases.
- WP+ Edition (Premium): updated the whitelist of webhook IP addresses of payment processors.
- Updated Chartjs library.
- Small fixes and adjustments.
4.8.2
- Fixed a “No such file or directory” PHP error due to a wrong path to the session folder (props @gosuccess).
4.8.1
- All active installations will now use NinjaFirewall sessions instead of PHP’s.
- Added compatibility with PHP 8.5, which will be released in a few weeks.
4.8
- All new installations will now use NinjaFirewall sessions instead of PHP’s. Current installations will automatically migrate at a later time (next release or so).
- Whitelisted reCAPTCHA response to prevent it from being blocked by the firewall.
- WP+ Edition (Premium): Updated the IP location databases.
- WP+ Edition (Premium): Added the PROPFIND method to the “Access Control > HTTP Methods” section. By default, it is not enabled.
- Updated Charts.js library.
- Added the “autofocus” attribute to the login protection form.
- Fixed a potential database issue: since PHP 8.1 MySQLi extension throws an Exception on errors (props @m2e47).
- Small fixes and adjustments.
4.7.5
- Several small fixes and adjustments under the hood.
- WP+ Edition (Premium): The firewall log can now be sorted in ascending (oldest entries first) or descending (newest entries first) order. See “NinjaFirewall > Logs > Log Options > Sorting”.
- WP+ Edition (Premium): Added Square and Airwallex webhook IP addresses to the “Access Control > IP address > External Services” section.
- WP+ Edition (Premium): When saving an IP address to the whitelist or blacklist in the “IP Access Control” settings page, NinjaFirewall will reject non-conform CIDR values and display a warning.
- WP+ Edition (Premium): Updated geolocation database.
4.7.4
- Fixed a bug where, in some cases, NinjaFirewall’s email notifications were not sent to all recipients but only to the first one in the list.
- Updated Charts.js.
- WP+ Edition (Premium): Updated geolocation databases.
- Small fixes and adjustments.
4.7.3
- Fixed the “[NinjaFirewall]” subject tag line that was missing in all email notifications.
4.7.2
- The email notification system was fully rewritten. You can now customize the subject and body of each email sent by NinjaFirewall. See our blog for more info about that: https://nin.link/nfmail
- Fixed a PHP “Uncaught Error: Undefined constant NF_PG_SIGNATURE” error.
- Fixed a PHP “ctype_digit(): Argument of type int will be interpreted as string in the future” notice.
- Fixed a PHP “Undefined array key REMOTE_ADDR” warning that could be returned by some command line cron jobs.
- Fixed a critical error with the saved “Custom HTTP headers” field on servers that supports HTTP/3.
- WP+ Edition (Premium): Added a check to the firewall so that if the plugin configuration is corrupted, the file size check will be skipped to prevent blocking uploads.
- Fixed some typos.
- Updated Charts.js.
- WP+ Edition (Premium): Updated GeoIP databases.
- Many small fixes and adjustments.
4.7
- This new version introduces NinjaFirewall sessions, an alternative to PHP sessions. They are an hybrid of PHP sessions and object caching, without session blocking. If you want to switch between PHP sessions and NinjaFirewall sessions, go to “NinjaFirewall > Dashboard” and follow the instructions.
- Fixed a “Undefined constant NFW_RULES” fatal error when migrating NinjaFirewall to another host.
- We have a new API (updates, security rules etc): api.nintechnet.com. Make sure to whitelist this subdomain if you are filtering outgoing connections.
- Updated Charts.js.
- WP+ Edition (Premium): Updated GeoIP databases.
4.6.1
- WP+ Edition (Premium): You can now enter your license key from WP CLI. Type “wp ninjafirewall license” and enter your license at the prompt.
- Fixed an issue with bulk user deletion: when multiple users were deleted at once, only the first one was written to the firewall log.
- Fixed an issue with the login protection: after disabling it and logging out, NinjaFirewall was still displaying a notice on the login page.
- Fixed a potential PHP fatal error: Attempt to modify property “no_update” on bool.
- Replaced all calls to the PHP glob() function with DirectoryIterator() to make file search compatible with remote files.
- Fixed an issue where some scheduled tasks were executed too often on multisite installations.
- WP+ Edition (Premium): Updated GeoIP databases.
- Updated Charts.js.
- Many additional small fixes and adjustments.
4.5.11
- Updated Charts.js.
- WP+ Edition (Premium): updated PayPal IPN and Automattic IP addresses.
- WP+ Edition (Premium): Updated GeoIP databases.
- Small fixes and adjustments.
4.5.10
- Added compatibility with blogs that don’t have a database prefix.
- In the “Custom HTTP headers” section, NinjaFirewall will automatically convert header names to lowercase.
- Fixed a potential “Timezone ID is invalid” PHP notice when viewing the log.
- Updated Charts.js library.
- WP+ Edition (Premium): Updated GeoIP databases.
- Small fixes and adjustments.
4.5.9
- Added a new policy to protect against user accounts deletion. It can be found in the “Firewall Policies > WordPress > Permissions” section.
- Fixed an issue with the firewall log where the time and date could be using the wrong timezone.
- Fixed a PHP deprecated notice in the sodium_crypto_generichash function.
- WP+ Edition (Premium): Fixed a bug in the firewall where some uploaded images could be wrongly blocked.
- Updated Charts.js library.
- Small fixes and adjustments.
- WP+ Edition (Premium): Updated GeoIP databases.
4.5.8
- Added a “Line wrapping” checkbox in the “Live Log” page: it can be used to wrap or unwrap the lines in the textarea field.
- Updated Charts.js library.
- Small fixes and adjustments.
- WP+ Edition (Premium): Updated GeoIP databases.
4.5.7
- You can now select to block access to the REST API only if the user is not authenticated. See “Firewall Policies > WordPress REST API > Allow logged-in users to access the API”.
- Fixed an accessibility issue with the toggle switches used in NinjaFirewall’s settings. They were not compatible with screen readers.
- Added a new constant that can be used to change the frequency used by the firewall to monitor the database:
NFW_DBCHECK_INTERVAL. It can be added to the wp-config.php or .htninja script. For instance, a 300-second interval:define('NFW_DBCHECK_INTERVAL', 300);. The lowest possible value, which is also the default, is 60 seconds. - Small fixes and adjustments.
- WP+ Edition (Premium): Updated GeoIP databases.
4.5.6
- WP+ Edition (Premium): Updated GeoIP databases.
- Updated Charts.js library.
- Small fixes and adjustments.
4.5.5
- NinjaFirewall will always rely on the timezone that was set by WordPress and PHP, and will no longer attempt to set it.
- Updated Charts.js library.
- Small fixes and adjustments.
- WP+ Edition (Premium): Updated GeoIP databases.
4.5.4
- Fixed a potential “syntax error” on sites running PHP <=7.2.
- Fixed a bug where quotes in “Custom HTTP headers” values were escaped with slashes.
- Updated Charts.js library.
- WP+ Edition (Premium): Updated GeoIP databases.
- Small fixes and adjustments.
4.5.2
- Fixed several deprecated messages on websites running PHP 8.1.
- Updated Charts.js library.
- Small fixes and adjustments.
- WP+ Edition (Premium): Updated GeoIP databases.
4.5.1
- Fixed a PHP “Cannot use object of type WP_Error as array” error.
- Activating/deactivating NinjaFirewall from WP CLI doesn’t require the
--userparameter anymore. - On websites running PHP 7.3 or above, NinjaFirewall will use the hrtime() function instead of microtime() for its metrics, because it is more reliable as it is not based on the internal system clock.
- WP+ Edition (Premium): Fixed a bug with right-to-left (RTL) WordPress sites where the checkboxes below the log were all messed up.
- The detection of base64-encoded injection has been slightly tweaked to lower the risk of false positives.
- WP+ Edition (Premium): The Bot Access Control input now accepts the following 6 additional characters:
( ) , ; ' ". - The “Monthly Statistics” graph and tooltip colours were improved.
- Updated Charts.js library.
- Small fixes and adjustments.
- WP+ Edition (Premium): Updated GeoIP databases.
4.5
- Added the possibility to enter custom HTTP response headers. See “Firewall Policies > Advanced Policies > HTTP response headers > Custom HTTP headers”.
- Added the possibility to view the server’s HTTP response headers. Click on the “Firewall Policies > Advanced Policies > HTTP response headers > HTTP headers test” button.
- Added a warning if WordPress is running inside a Docker image and the user wants to upgrade NinjaFirewall to Full WAF mode.
- Fixed a PHP “Undefined array key pluginzip” warning when reinstalling a plugin from a ZIP archive.
- WP+ Edition (Premium): The Access Control URI whitelist and blacklist now support permalinks.
- Fixed an issue where the daily report could be sent multiple times on some multisite installations.
- Fixed deprecated readonly() function message on WordPress 5.9.
- Fixed an issue where the firewall would wrongly send a WordPress update notification.
- WP+ Edition (Premium): Updated Stripes webhook notifications IP addresses in the Access Control section.
- Updated Charts.js library.
- WP+ Edition (Premium): Updated GeoIP databases.
- Many small fixes and adjustments.